Continuous Compliance & Sovereign Governance

Augur | Continuous Compliance & Sovereign Governance Architecture

Automating operational proof and continuous attestation across high-stakes autonomous systems. Augur continuously verifies code, infrastructure state, and operational telemetry against global regulatory mandates with mathematical certainty.
C# / .NET 10Blazor ServerEF CoreOpenAPI 3.1.1
Request Institutional Assessment
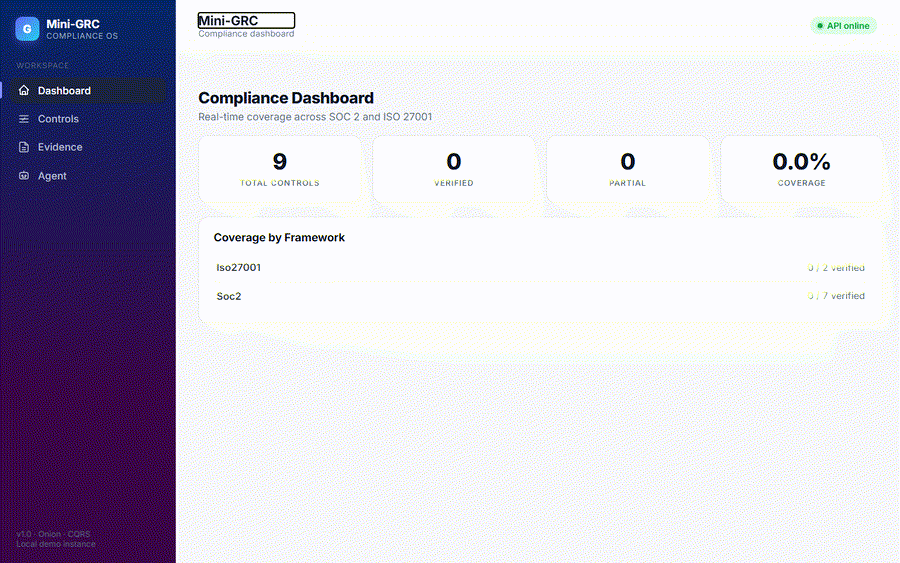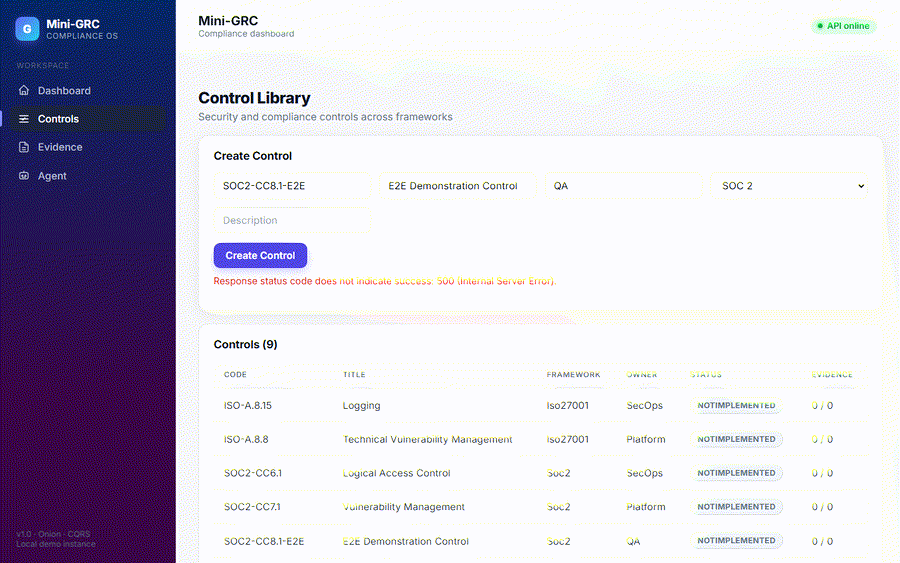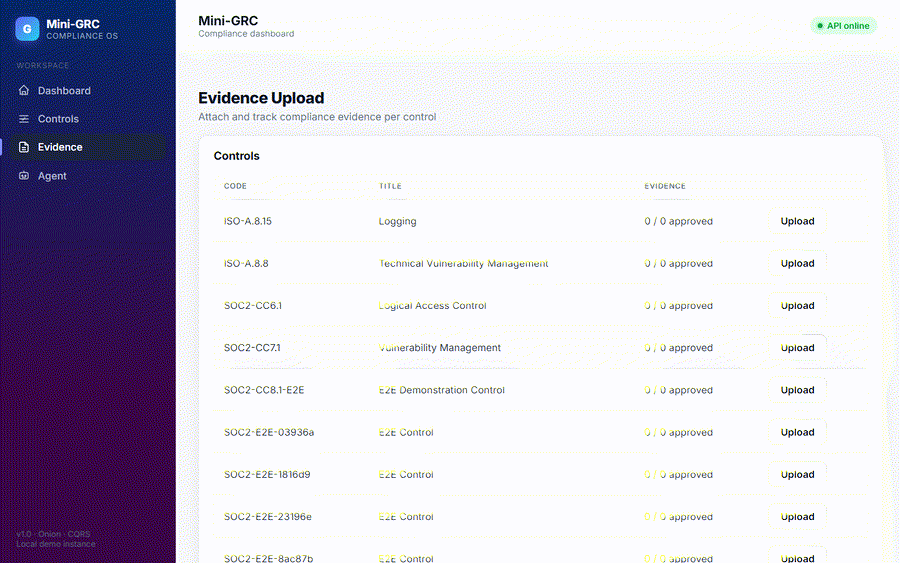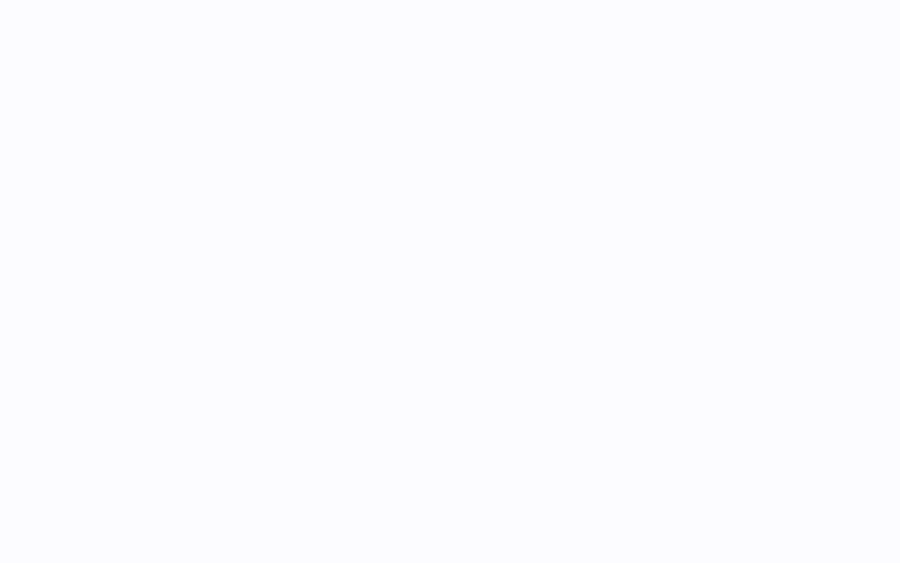
Augur Compliance Automation Demo
Live Compliance MappingBlazor WebUI
Audit Latency
< 15 Minutes
From telemetry emit to sealed proof
Control Resolution
Deterministic
Zero heuristic sampling bias
Perimeter Boundary
Zero-Exfiltration
Cryptographic hashes only
Assurance Model
Continuous
Real-time point-in-time seals

Deterministic Control Mapping

Dynamic, bidirectional compilation between code diffs, container lifecycles, and discrete regulatory controls. Every pull request and Terraform change is automatically indexed directly against applicable SOC 2 and ISO criteria.

Continuous Evidentiary Ledger

Eliminate reactive quarterly audit prep. Augur replaces manual screenshot evidence collections with an automated, tamper-proof evidentiary ledger continuously compiled and verifiable at any arbitrary timestamp.

High Performance .NET 10 Enclave

Engineered with C# .NET 10, Entity Framework Core, and Blazor Server for low-latency streaming compliance updates across thousands of repositories.

Interactive Tool

Augur Auto-Mapper Simulator

Select a sample security finding below to test Augur's control mapping engine in real time.

FIND-101HIGH
S3 Bucket Encryption Disabled
Production S3 bucket `prod-data-vault` has SSE-KMS customer managed encryption unconfigured.
FIND-102CRITICAL
MFA Enforcement Missing for Admin Role
IAM Role `DevOpsAdminRole` allows assumeRole without requiring multi-factor authentication token.
FIND-103HIGH
Outdated Dependency CVE-2024-3094
Library `xz-utils` version 5.6.0 detected in container image `api-gateway:latest`.
AUGUR_ENGINE_OUTPUT // FIND-101CONFIDENCE: 99.4%
Primary SOC 2 Control Mapping:
CC6.1 - Logical Access Controls & CC6.7 - Data Transmission Encryption
ISO 27001:2022 Mapping:
ISO 27001:2022 A.8.24 - Use of Cryptography
Suggested Policy Enforcement:
POL-SEC-04: Data Classification and Storage Protection Policy
Audit Trail Rationale:
Unencrypted storage exposes stored customer assets. Policy mandates AES-256 or KMS-based envelope encryption on all static datastores.
OpenAPI 3.1.1 Export ReadyResponse time: 14ms
[05] Engagement

Request Institutional Assessment

Deploy Augur within sovereign infrastructure in under 48 hours. Our engineering directors engage directly with your Chief Information Security Officer and governance leads to model continuous control attestation across your infrastructure surface.

Available on-premise, AWS GovCloud, or sovereign VPC
Includes baseline gap analysis against SOC 2 & ISO 27001
Direct access to core systems engineering personnel

Subject to mutual non-disclosure. Zero third-party telemetry transmitted.